Miss a Cyber Awareness Month event?
No problem! Check out our recorded sessions.
- Cyber Awareness Month Kick-off and a year in review
- Identity offboarding — Closing the door behind us
- Endpoint protection on campus: SentinelOne and Tenable
- Cybersecurity at home and beyond
- Cybersecurity for researchers: Supporting secure research
- Halloween Haunt — The Canvas Breach (Shadow IT) Coming soon!
HONK! Welcome to the final week for Cyber Awareness Month!
This week marks the final Goose Guide for Cyber Awareness Month. Over the past three weeks, the Goose has shared lessons that help each member of the University community build their own digital resilience: securing your Waterloo digital home, watching for threats across campus, and sharing information safely in our shared spaces. Together, these practices reflect our personal responsibility for keeping ourselves, our information, and our community secure. Even as Cyber Awareness Month migrates with the geese to winter somewhere warm, there are still things we can learn from their departure.
Tip 4: Keeping the Waterloo community resilient
Every autumn, Canada geese prepare for one of nature's most remarkable journeys. Flying thousands of kilometres requires more than strong wings. Geese learn migration routes from experienced members of the flock, prepare for the challenges ahead, and adapt when conditions change. Cybersecurity resilience works much the same way. A resilient community learns from those with experience, prepares before problems occur, responds when conditions change, and recovers when something goes wrong.
Learn
Geese that have never made the journey rely on those who have. Migration routes, hazards, and survival habits are passed down through the flock, because relying on experience is safer than learning the hard way, mid-flight. But experience alone isn't enough. Routes shift, conditions change, and even the most seasoned geese can't rely only on what they learned last season. The flock survives by continuing to learn, year after year, not by assuming last year's knowledge still holds.
Cybersecurity works the same way. New scams, technologies, and risks emerge constantly, and even long-time members of the Waterloo community can't rely only on what they already know. The more we learn — and keep learning — the better prepared we are for the journey ahead.
Learn from the flock by:
- Completing annual cyber awareness training.
- Subscribing to Honk If You're Secure! for timely Goose Guide tips and Tales from the SOC, which use real Waterloo incidents to help us recognize threats and avoid repeat mistakes.
- Reading the Cyber Awareness website resources.
- Reviewing University IT Security Standards.
- Knowing how to spot and report suspicious emails, activity, or security concerns to the SOC.
Prepare
Geese prepare for the unexpected by building continuity into the flock. The lead goose faces the greatest resistance and cannot hold that position forever. When it tires, another goose immediately takes its place, allowing the flock to continue its journey without interruption. The flock does not stop moving because a critical component becomes unavailable; it already has a replacement ready.
Cybersecurity preparation follows the same principle. While incidents, outages, and disruptions cannot always be prevented, their impact can be reduced through backups, redundancy, and recovery planning. Just as geese rely on replacement leaders to keep the flock moving, Waterloo relies on backups, failover systems, and tested recovery procedures to keep critical services available when something goes wrong.
Prepare for the unexpected by:
- Maintaining and testing reliable backups.
- Keeping an inventory of what data you have, where it is stored, and who should have access to it.
- Documenting how access can be restricted, or systems can be taken offline if they need to be investigated.
- Having a continuity plan for critical services appropriate to their importance and impact.
- Knowing who to contact during a security incident. Resilient communities are not built when an incident happens. They are built beforehand.
Respond
Storms, predators, and changing conditions may force the geese to alter course mid-flight.
Every flock relies on members who have made the journey before, who know which routes are safe, where the hazards lie, and how conditions can shift along the way. Birds near the back may not see danger ahead, but the flock trusts the ones at the front and adapts when they change direction, not because of hierarchy, but because that knowledge keeps everyone safe.
The same is true during a cybersecurity incident. Waterloo's security team plays that role for our digital flock. Information Security Services tracks the threats, vulnerabilities, and active security events most of us never see, so when they ask the community to act, it's worth listening.
You may be asked to:
- Apply emergency security updates
- Change passwords or reset credentials
- Disconnect affected devices from the network
- Stop the use of compromised accounts or systems
- Follow containment measures to limit the spread of an incident
These requests are not made without reason. When the flock changes course, adapting quickly helps protect everyone.
Recover
Even successful migrations encounter challenges. After a storm, the flock regroups, recalibrates, and continues the journey using what it has learned.
Cyber resilience is not measured by whether an incident occurs. It is measured by how effectively we recover when one does.
Recovery may include:
- Restoring data from backups and validating critical information.
- Rebuilding, reimaging, or recovering affected systems and services.
- Reviewing logs, evidence, and incident details to understand what happened.
- Supporting investigations and reporting fraud, identity theft, or other impacts when required.
- Returning operations to normal and communicating recovery status.
- Applying lessons learned to strengthen future resilience and preparedness.
Every incident provides an opportunity to improve the next journey.
The Final Honk
As Cyber Awareness Month comes to a close, the Goose's final lesson is simple: cybersecurity is not a destination. It is a journey, but not a journey any single goose makes alone. Cybersecurity is a shared responsibility. The strongest flocks succeed because every member plays a part. They learn, prepare for challenges, respond when conditions change, and recover when obstacles appear. By carrying these habits forward throughout the year, we can help build a more resilient Waterloo community.
Keep learning, preparing, responding, recovering, and of course, keep Honking!
Want to learn more about Canada's most secure campus residents?
HONK! Welcome back to Cyber Awareness Month!
Last week, the Goose taught us about the importance of the campus watch and the PAUSE framework. By staying alert for danger and honking to warn the flock, geese remind us that cybersecurity is a shared responsibility.
Tip 3: Share safely in our shared spaces
This week, the Goose focuses on protecting what matters. Just as geese control access to nests, goslings, and other important spaces, information should be protected based on its value and sensitivity. Under Policy 46, information is classified to help determine who should have access, where it belongs, and how it should be shared. For more information, see the Guidance on Information Confidentiality Classification (Policy 46).
Classify first
Public information: Digital footprints
Geese leave footprints wherever they travel. A trail of webbed footprints can tell a story about where the flock has been, where it spends its time, and where it might be headed next.
We leave tracks, too. Everything we share publicly contributes to our digital footprint. Social media posts, public websites, conference presentations, online profiles, and forum discussions can reveal information about our interests, activities, relationships, routines, and work.
For more tips on managing your online presence, see Protect Your Privacy on Social Media Platforms.
Confidential information: Grazing grounds
Geese gather on the grazing grounds to eat and rest. While they remain watchful, they generally allow other geese and even people to pass through without triggering the same defensive response seen closer to the nest. The area is still important to the flock, but it is a shared space rather than a tightly controlled one.
Likewise, confidential information is intended for a specific audience but would generally not cause the same level of harm as restricted or highly restricted information if disclosed.
The primary concern is often loss of control rather than direct harm. Draft course materials, department meeting notes, subscription-based research resources such as PubMed, purchased digital content, or information released through a formal access process may have value because access is intentionally limited to a particular group. Confidential information can often be shared among authorized users without requiring extensive controls. Problems arise when the information spreads beyond the intended audience. Once shared publicly, redistributed, or provided to an unapproved third party, the owner may lose control over how the information is used, reused, or further shared.
Restricted information: Goslings
Unlike footprints left behind or feeding grounds shared with the flock, geese become much more protective when goslings are involved. While goslings can move on their own and respond to danger, they are still vulnerable and depend on the flock to keep them safe. Restricted information deserves the same level of care.
The University has an obligation to protect information such as student grades and accommodation records, employee information, research data governed by ethics approvals or research agreements, and information covered by contracts or non-disclosure agreements.
These obligations may come from privacy legislation, contractual commitments, research agreements, or other legal and regulatory requirements. Failing to meet these obligations can harm the individuals whose information has been entrusted to us and may result in legal, contractual, financial, operational, or reputational consequences for the University.
Highly Restricted information: The eggs
Nothing gets a goose's attention faster than someone approaching its eggs. Unlike goslings, eggs cannot move away from danger or protect themselves. They are vulnerable, irreplaceable, and critical to the future of the flock. Geese defend them aggressively because the consequences of losing them can be severe.
Highly Restricted information deserves the highest level of protection for the same reason.
If this information is exposed, stolen, or misused, the consequences can be immediate and significant. Individuals may experience identity theft, financial fraud, loss of medical privacy, or other serious harms. The University may face security incidents, regulatory consequences, or the loss of highly classified research.
Share only with the right people
Geese do not treat every visitor the same way. Information sharing should be managed in a similar way, based on its classification, who needs access, and the potential impact if it were exposed.
Before sharing information, consider whether the recipient truly needs access and choose an appropriate sharing method.
When sharing outside the University, follow the guidelines for secure data exchange. Review access regularly and remove permissions that are no longer needed.
Choosing where information belongs
Once you know who should have access, the next step is choosing where information belongs. Geese choose where to gather based on what they are protecting. Open areas are suitable for activities visible to the whole flock, while nests provide a protected environment for what is most sensitive.
The same principle applies to information. Choosing the right storage location helps ensure that information is available to the right people while remaining appropriately protected.
Review and clean up
Information often remains valuable long after the person who created it has moved on. Storing information in team-managed spaces rather than personal storage helps ensure appropriate access, continuity, and long-term stewardship. For more information, see When to Choose OneDrive, Teams, or SharePoint Online.
Waterloo’s department of Information Systems & Technology (IST) also provides a Data Storage Solutions support tool designed to help you explore available data storage solutions.
Pro tip: When information is no longer needed, it should be disposed of according to University retention requirements. Information that has been securely deleted and disposed of cannot be exposed in a future breach.
Sharing information with AI
AI tools introduce a different consideration. Rather than sharing information with people, you are sharing it with a system that processes, analyzes, and generates content based on the information you provide. The challenge is not always the immediate exposure of information. Sometimes the greater concern is loss of control. Once information is shared with an unapproved AI tool, it may be stored, retained, reused, or incorporated into systems in ways that were not originally intended.
Geese approach unfamiliar situations cautiously. As AI tools continue to evolve, we should do the same by considering what information we share, whether a tool is approved, and the potential risks involved.
The University provides Enterprise Copilot as the approved AI service for University work. Other AI tools, including AI features in existing applications and third-party meeting bots, may not be approved for the information you intend to share.
Before using University information with an AI tool, ensure the tool is approved for the information you intend to share and review Waterloo's AI Safeguarding Tips. New AI tools and features should be reviewed through the AI Approval & Support process before use.
Before sharing information with an unapproved AI tool, ask yourself, Would I be comfortable if I lost control of this information or if it became public?
The Goose's Share Safely Checklist
- Classify the information before storing or sharing it.
- Review your public information and digital footprint.
- Confirm the recipient has a legitimate need for access.
- Choose a storage location that matches the information's classification.
- Review sharing permissions and remove unnecessary access.
- Verify that an AI tool is approved before sharing University information.
Want to learn more about Canada's most secure campus residents?
HONK! Welcome back to Cyber Awareness Month!
Last week, the Goose taught us how to build a secure digital home through security by design, in depth, and detailing. This week, the Goose is back with another lesson from the flock: the importance of a campus watch!
Tip 2: Campus Watch | Stay alert, PAUSE, and honk for the flock!
Every spring, members of the University of Waterloo community become familiar with another well-known goose behaviour: vigilance. Whether protecting a nest, grazing with the flock, or watching over goslings, geese are constantly aware of what is happening around them. A strong digital community works the same way. Cybersecurity is more than individual security habits. It depends on all of us staying alert, recognizing threats, and helping protect the broader Waterloo community.
Stay alert
Most attempts rely on the tactics of impersonation, deception, or pressure.
Geese don't watch for just one type of threat. They stay aware of anything unusual that could put the flock at risk. While phishing remains one of the most common threats facing the Waterloo community, modern attacks often use AI, reference real Waterloo systems, and may even come from compromised University accounts.
- Impersonation: Attackers pretend to be a trusted person or entity.
- A message appears to come from Workday, Quest, LEARN, Microsoft 365, or another University service.
- A Business Email Compromise (BEC) message appears to come from a colleague, manager, instructor, researcher, Dean, or Department Chair.
- AI-generated audio, video, or messages impersonating real people.
- Emails, phone calls, or text messages claiming to be from law enforcement, immigration services, or the Canada Revenue Agency (CRA).
- Deception: Attackers trick you into giving away information or access.
- Fake WatIAM login pages designed to steal credentials or Duo verification codes.
- Text messages and phone calls claiming to be from technology support, financial institutions, delivery companies, employers, or government agencies.
- Phony receipts for services you supposedly purchased, sent via email or text message, encouraging you to call or email to discuss the charge.
- Pressure: Attackers try to rush your decision-making.
- Urgent requests to approve a Duo 2FA login.
- Messages claiming your account will be suspended.
- Requests to purchase gift cards, transfer funds, or bypass normal processes.
A vigilant goose doesn't react to every movement immediately. It watches, assesses the situation, and decides whether a threat is present. The same principle applies when you receive an unexpected email, message, attachment, login request, or financial request. Use the PAUSE framework:
- P – Pause: Take a breath and interrupt the urge to react immediately. A message demanding immediate action is often trying to influence your decision-making.
- A – Awareness: Pay attention to how the message makes you feel. Does it create urgency, fear, excitement, or pressure? Emotional reactions can be warning signs that someone is trying to manipulate you.
- U – Unpack the Message: Look beyond the request. Is the sender legitimate, does the request make sense, and are you being asked to do something unusual, urgent, or outside your normal role?
- S – Select the Next Step: Decide how to respond. Verify through a trusted channel, navigate to a known website, seek a second opinion, or choose not to proceed. Don't let the attacker decide your next step.
- E – Escalate: Report suspicious emails, scams, fraud, or account compromises to the Security Operations Centre (SOC) or appropriate organization immediately. Early reporting protects both you and others who may be affected.
PAUSE before you act
Before clicking, replying, downloading, or approving access, use the PAUSE framework.
HONK for the flock
Early reporting helps contain the problem and protect others.
One of the most recognizable things about geese is how they communicate. When a goose detects danger, it honks, alerts nearby geese, and helps protect the flock.
Reporting suspicious emails, unexpected Duo prompts, unusual account activity, fake WatIAM login pages, or other security concerns helps protect the Waterloo community in the same way. A threat reported by one person may prevent many others from being affected.
If something seems suspicious, report it to the Security Operations Centre (SOC). Whenever possible, submit phishing messages as an attached email, so investigators can review the original message and technical details.
Whether or not you clicked the link, opened the attachment, entered information, or approved a login request, report it anyway.
The Goose's Campus Watch Action Plan
- Learn how to defend against phishing at Waterloo.
- Practice the PAUSE framework before responding to unexpected requests.
- Save the SOC contact information so you know where to report concerns.
- Report suspicious emails, Duo prompts, or account activity when you encounter them.
- Learn how to submit suspicious emails as attachments.
- If you think you've made a mistake, report it anyway!
Want to learn more about Canada's most secure campus residents?
Tip 1: Secure Your Digital Environment at Waterloo and Beyond
This week, the Goose focuses on the nest. A secure home doesn't happen by accident. Geese carefully build their nests, protect what matters most, and maintain them throughout the season. Our digital homes require the same approach through the three Ds of a Secure Nest: Security by Design, Security in Depth, and Security Detailing.
Security by design
Consider the risks first
Before building a nest, a goose evaluates its surroundings. Although many of us have encountered a goose nesting in a location that seems completely impractical, geese don't choose their nests at random. They prefer locations where they can see potential threats coming and protect what matters most. Security starts long before the first twig is placed.
The same principle applies at the University of Waterloo. Before introducing a new application, AI tool, service, or process that will access University information, consider the risks first. What information will it collect? Where will that information be stored? Who will have access to it? At Waterloo, if a tool will access restricted, highly restricted, or personal information, additional review may be required. If you're unsure how information is classified, refer to Waterloo's Information Confidentiality Classification Guidance. For initiatives involving these types of information, Information Risk Assessments (IRAs) and Privacy Impact Assessments (PIAs) help identify and address risks before implementation.
The same mindset applies beyond Waterloo. Before signing up for a new online service, mobile app, or AI tool, review the privacy practices and consider whether the service really needs access to your contacts, photos, location, or other personal information. The Office of the Privacy Commissioner of Canada provides guidance on protecting your privacy online. A few minutes of research before adopting a new tool can help prevent privacy and security issues later.
Cybersecurity works the same way. Whether you're protecting your WatIAM account, a University service, or a personal account beyond Waterloo, no single security control can protect everything.
Start with strong, unique passwords. Waterloo's Password Standard recommends passwords of at least 15 characters for WatIAM accounts. Consider using a memorable passphrase, such as Cobra*Chickens!, rather than a shorter password, and avoid reusing passwords across multiple services. Password managers can help generate and securely store unique credentials for your WatIAM account, University services that do not use single sign-on (SSO), and your personal accounts. Once you've set up a password manager, consider removing passwords saved in browsers, notes, spreadsheets, or other locations that may not provide the same level of protection.
Add another layer with two-factor authentication (2FA). WatIAM accounts are protected by Duo 2FA, which can also be used to secure many personal accounts. Whether at Waterloo or beyond, enable 2FA wherever it is available and choose the strongest authentication method offered. App-based authenticators, security keys and passkeys generally provide stronger protection than email or text message (SMS) verification. Never share your passwords, 2FA codes, or authentication approvals with anyone.
Finally, protect the device itself. Device encryption provides yet another layer of protection by helping safeguard information if a laptop, phone, or storage device is lost or stolen, whether that device is University-managed or personally owned.
Security in depth
No single security control can protect everything
A goose doesn't build a nest from a single twig. Nests are constructed using grasses, reeds, moss, twigs, and down feathers, with each layer contributing to the strength and protection of the nest. While each material serves a different purpose, together they create a safer nest than any one material could provide on its own.
Security detailing
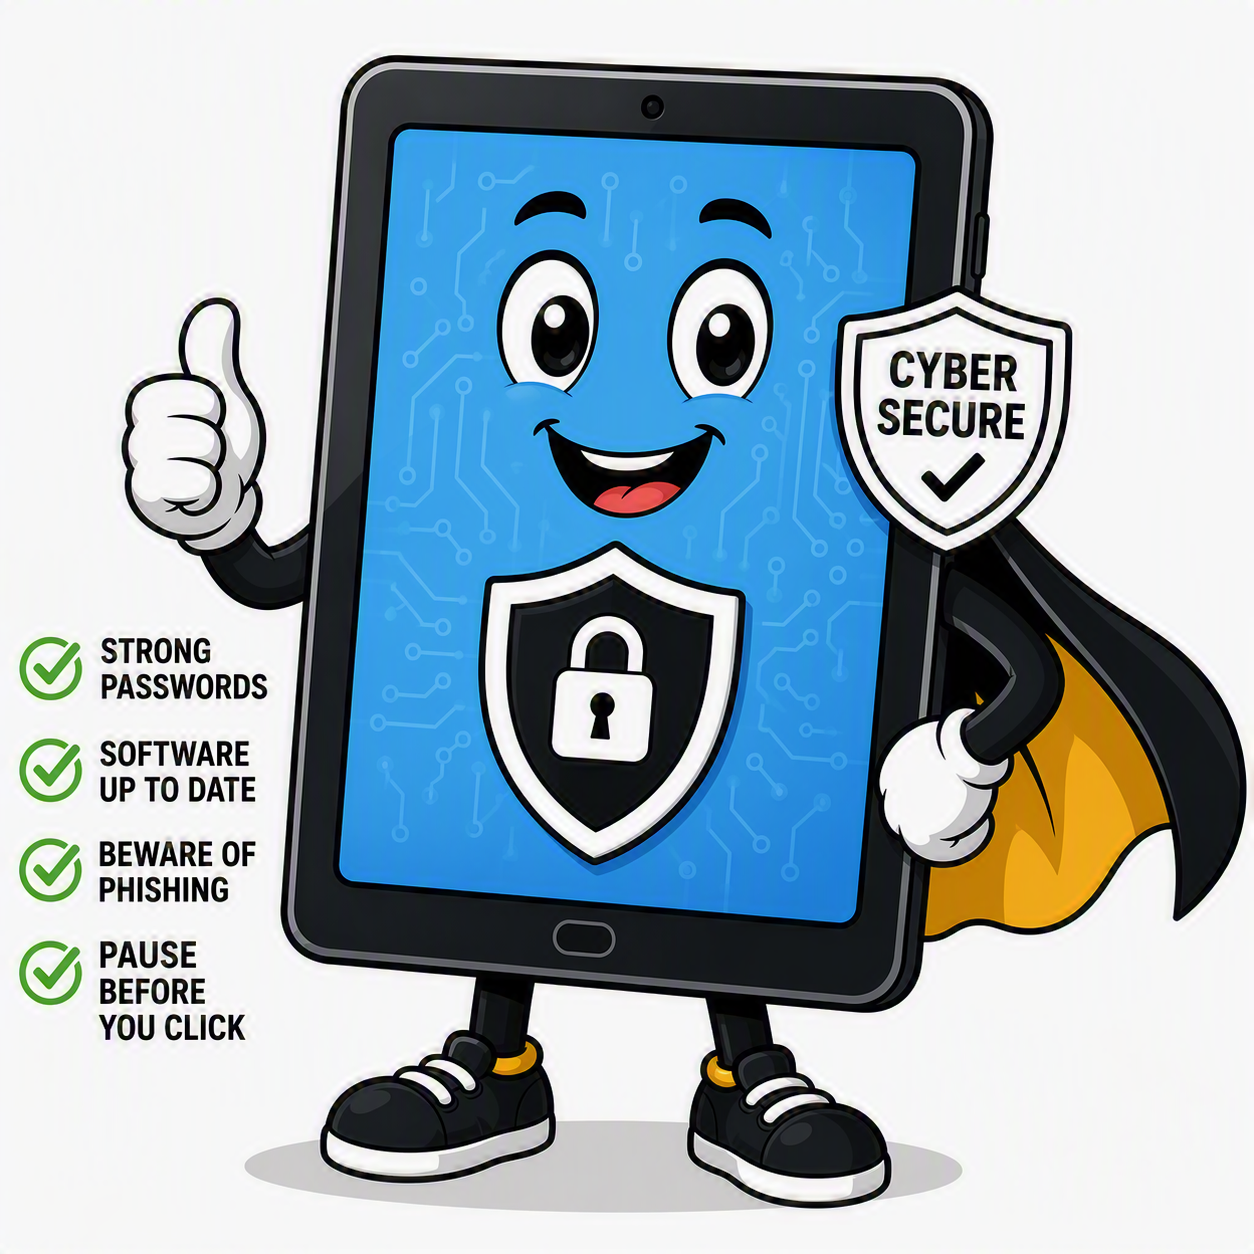
Updates often address vulnerabilities before they can be exploited
Building a nest is only the beginning. Throughout the season, geese repair damage, replace worn materials, remove debris, and deal with pests before they become a larger problem.
Whether you're using a University-managed or personal device, keeping software up to date is one of the simplest and most effective ways to maintain a healthy digital environment. Apply operating system, browser, application, and mobile device updates promptly, including optional security updates when recommended. These updates often address vulnerabilities before they can be exploited.
Behind the scenes, University-managed workstations and servers are also monitored using vulnerability management tools such as Tenable, which help identify systems that may require updates or remediation. Together, vulnerability management and timely patching help keep Waterloo systems healthy and secure.
Just as geese remove debris from their nests, periodically review applications and online accounts you no longer use. Removing unnecessary software and closing dormant accounts reduces your digital footprint and eliminates opportunities for attackers to exploit forgotten accounts.
And then there are the pests. A goose would never ignore signs that insects or other unwelcome visitors had moved into its nest. Malware behaves much the same way. Left unchecked, malicious software can spread, steal information, disrupt work, or provide attackers with access to systems.
To help detect and respond to these threats, University-managed devices use SentinelOne Endpoint Detection and Response (EDR) technology, which helps identify suspicious activity and malicious behaviour. For personally managed devices, consider using one of Waterloo's recommended endpoint security products for home use, pay attention to security warnings, and investigate unusual activity as soon as it is detected.
The Goose's Secure Digital Environment Checklist
Security by Design
-
Understand the risks before introducing a new tool, application, or AI service.
-
Complete an IRA or PIA when required.
Security in Depth
-
Use long (15+ characters), unique passphrases for your accounts.
-
Set up a password manager.
-
Enable 2FA and use the strongest method possible.
-
Enable device encryption.
Security Detailing
-
Install operating system, application, browser, and mobile device updates promptly.
-
Use a reputable endpoint protection for Waterloo and personal devices.
-
Remove applications and close accounts you no longer use.